AWS DevSecOps Automated Vulnerability Scanning & Blue/Green Pipeline
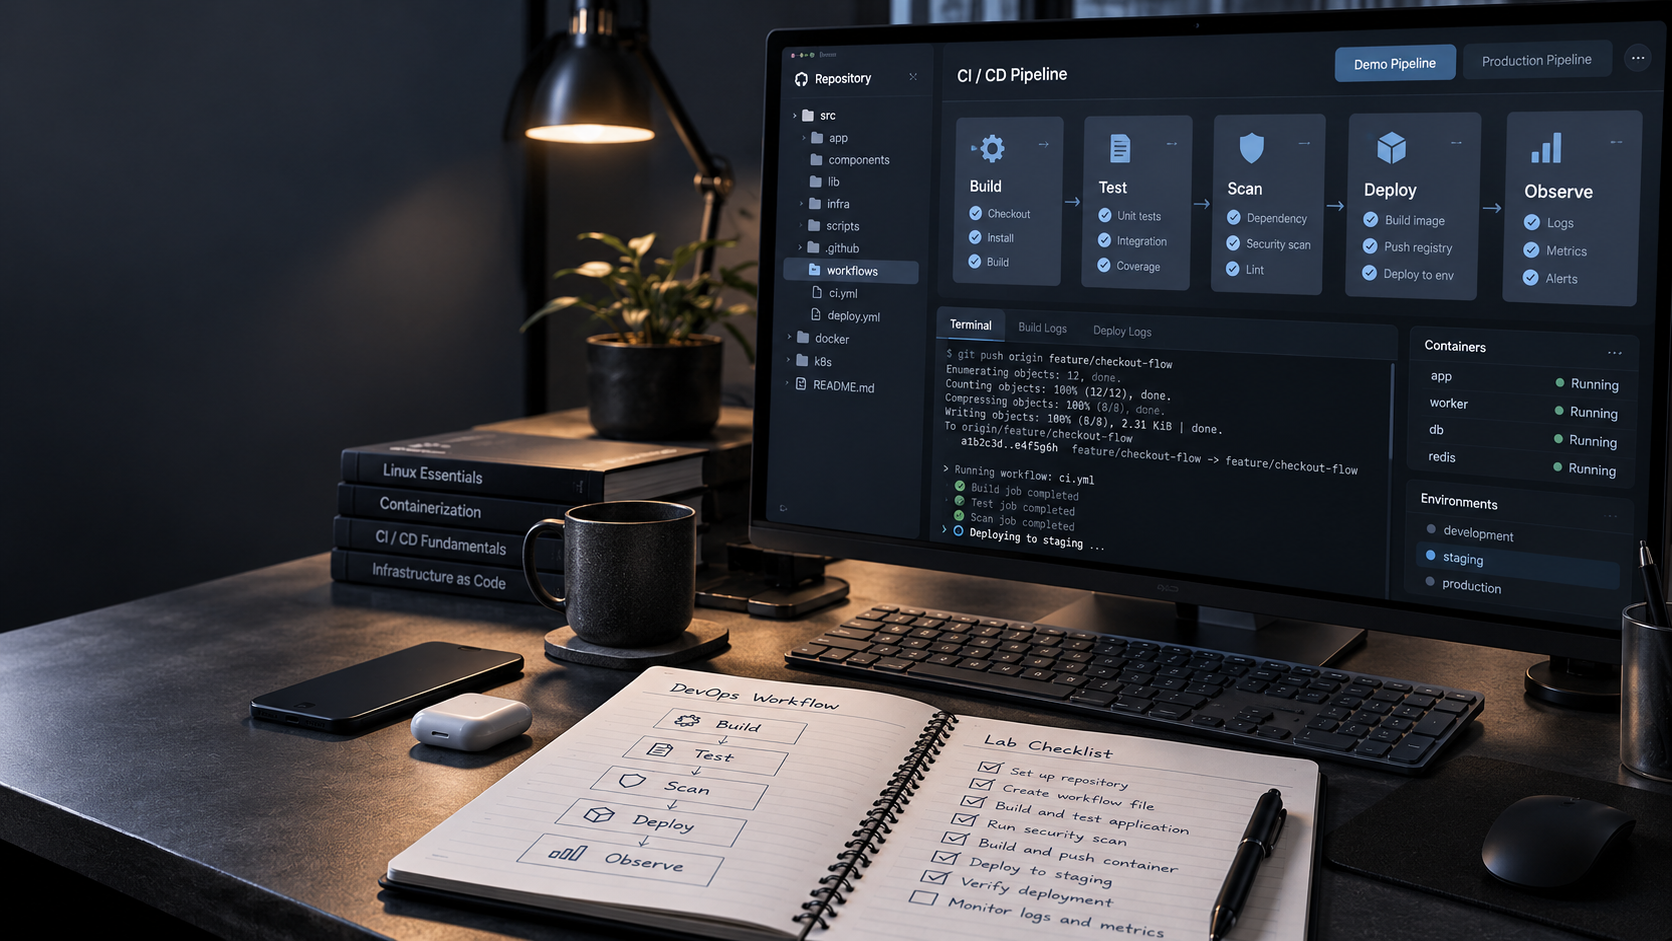
End-to-end automated DevSecOps continuous deployment pipeline on AWS ECS with zero-downtime blue/green execution, cryptographic image signing, and automated Trivy vulnerability gates.
CloudScale Logistics UK suffered from high-friction 45-minute manual release cycles where security checks were either skipped or created severe deployment bottlenecks across regional fulfillment depots.
Aravex Tech Studio engineered an automated Infrastructure as Code (IaC) pipeline in Terraform. Every commit triggers automated container SAST scanning, dependency vulnerability audit, and zero-downtime ECS task cutover with rollback telemetry.
Architecture & Topology
Key Capabilities
Technologies Employed
HAVE AN IDEA?
LET’S ARCHITECT IT.
From custom web platforms and offline POS systems to autonomous AI agents and zero-downtime cloud infrastructure — partner directly with lead systems architects who deliver.